Overview
KeyStrike Cloud Protector extends identity security by enforcing device-bound usage and full session protection, via continuous user presence validation, across SaaS applications. It integrates with your existing IdP (such as MS Entra ID) and requires no change to user login behavior.
How Attackers Compromise SaaS Access
Modern SaaS breaches begin with compromised credentials and end with stolen data, corrupted systems, and outages affecting revenue and reputation. While MFA protects from some threats, the advanced adversaries have moved onto breaching workstations to inherit your identity, access, and environment to blend their attacks with your legitimate activity.
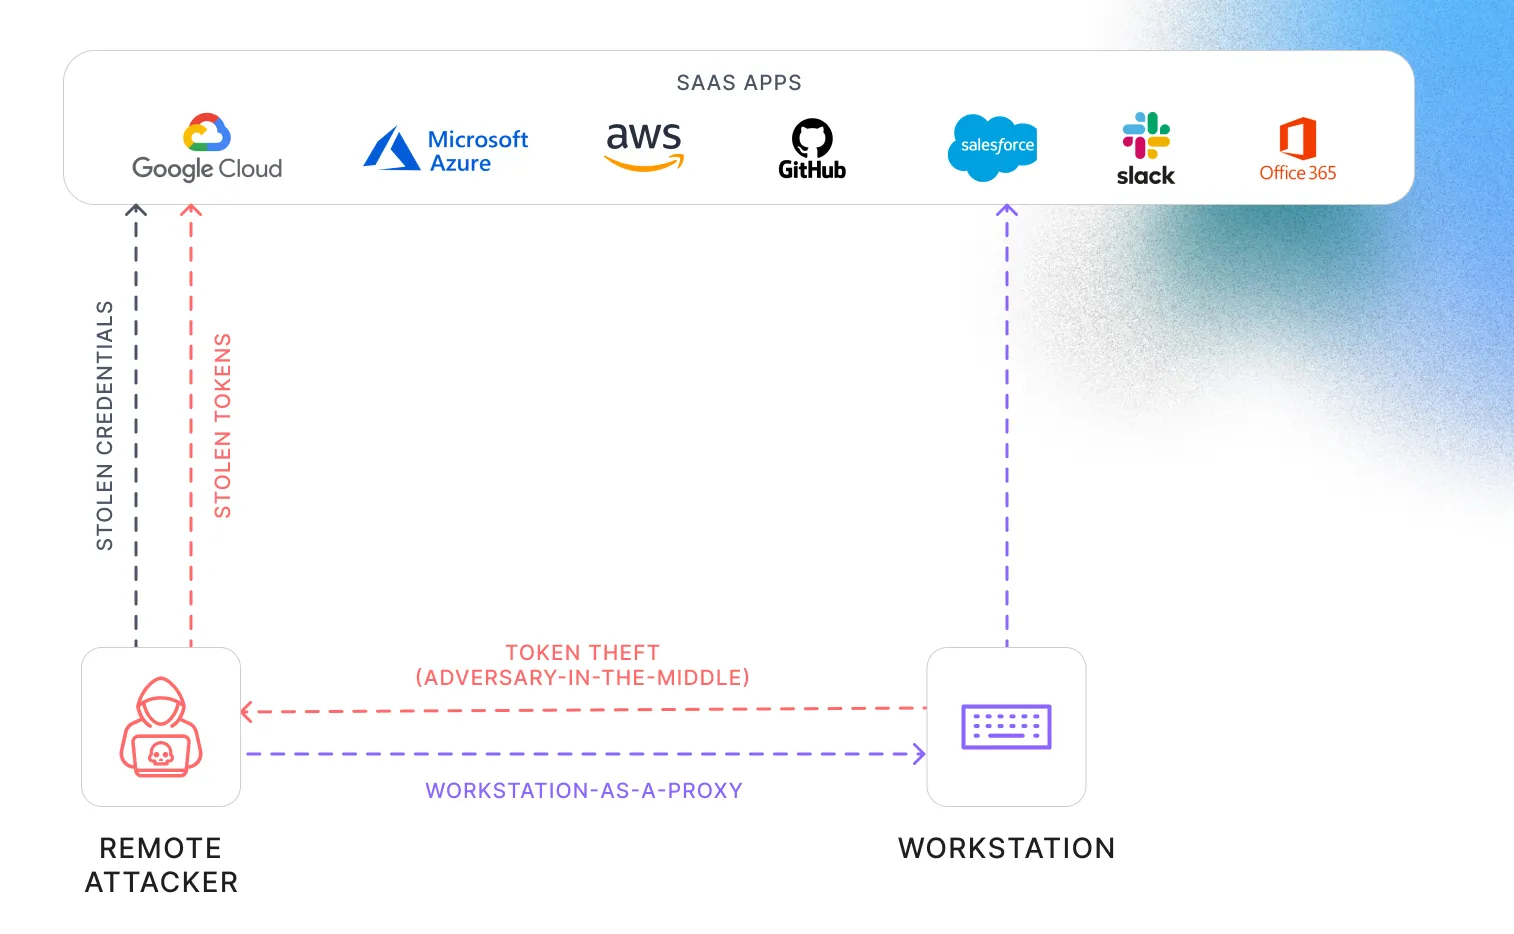
Stolen Credentials (Black dashed arrows)
This represents an attacker obtaining a user’s username and password for a SaaS application. Common ways attackers steal credentials include:
- Phishing emails or fake login pages
- Password reuse across sites
- Keyloggers
- Database breaches
Once the attacker has valid credentials, they can log in to services as if they were the user—unless other protections block them.
Stolen Tokens (Red dashed arrows)
Even if credentials aren’t stolen, an attacker can compromise session tokens. Session tokens are what keep a user logged in after MFA succeeds.
Threats here include:
- Token theft malware on a workstation
- Browser session hijacking
- Memory scraping
- Adversary-in-the-Middle (AiTM) attacks, where an attacker intercepts tokens during login
With the token, the attacker can bypass passwords and even MFA.
Workstation-as-a-Proxy (Purple dashed arrows)
Instead of stealing tokens outright, the attacker may:
- Use the victim’s workstation to proxy their authentication traffic
- Use Remote Access Trojans (RATs) or other remote-control tools
- Execute browser actions locally to avoid detection
This technique allows attackers to blend in as a “normal user” because:
- Requests originate from the real device
- IP and geolocation look legitimate
- Device posture appears normal
This defeats many behavioral and zero-trust systems.
Keystrike Cloud Protector
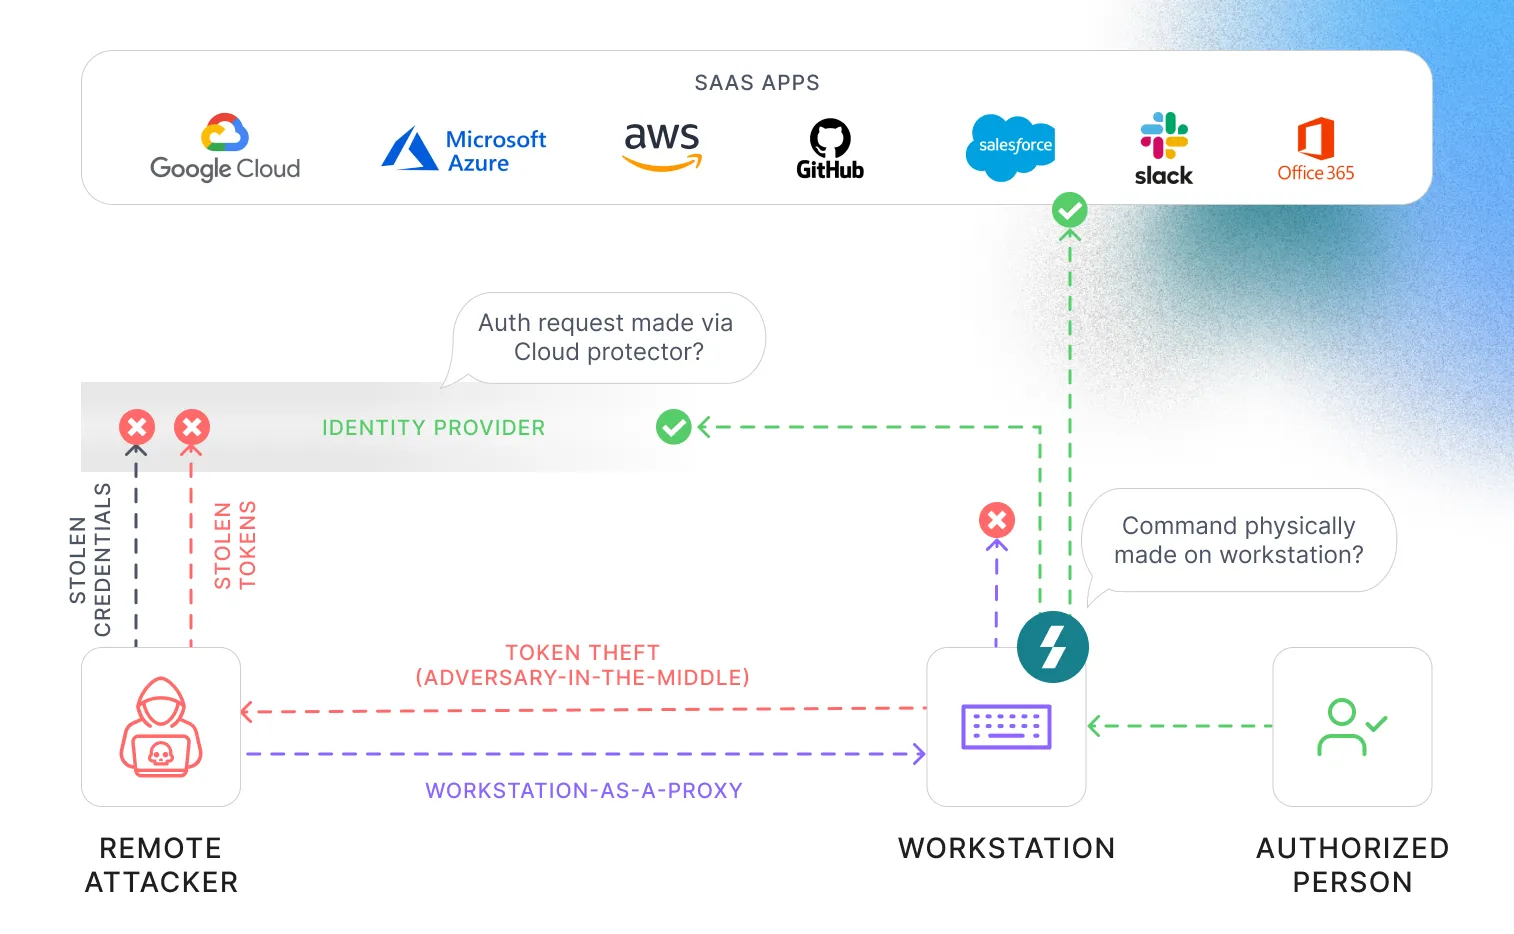
Device Bound Usage
Overview Device-Bound Usage ensures that every authentication attempt is cryptographically linked to a specific, trusted workstation. Even if an attacker obtains valid user credentials, cookies, or session tokens, they cannot use them from another device.
How It Works KeyStrike Cloud Protector is installed on authorized user workstations and securely bound to the device’s TPM (Windows) or Secure Enclave (macOS). This binding creates a hardware-backed identity for the workstation that cannot be cloned or exported.
The organization’s Identity Provider (IdP) is then configured with conditional access rules that enforce the following:
- All authentication requests must originate through KeyStrike Cloud Protector Unauthorized devices or remote attackers cannot directly authenticate to the IdP.
During authentication, Cloud Protector produces a device-bound proof that is validated by the IdP before the login is allowed. As a result:
- The authentication token becomes cryptographically bound to both the user account and the originating device.
- Tokens, cookies, or credentials stolen from the browser or disk cannot be reused from any other machine, even if an attacker has full possession of them.
Once authenticated, the user’s application session proceeds normally with no rerouting, proxying, or network performance impact.
Protection Level:
- Prevents stolen credential usage
- Prevents cross-device token reuse
- Prevents session replay from attacker-controlled systems
Full Session Protection
Overview For sensitive, privileged, or high-value SaaS applications, KeyStrike offers continuous session enforcement, verifying recent physical user input for every important request.
How It Works Unlike standard SSO, access to the application is not granted once and left unchecked. After authentication, requests to the web application must be accompanied by evidence of recent, valid user activity (such as keystrokes or mouse input). If no legitimate user input is detected in the application performing the request, the request is blocked.
This ensures that only a live, authorized user on a known device can maintain access.
Protection Level:
- Prevents session hijacking
- Prevents idle-device abuse (e.g., attacker using a workstation while user is away)
- Prevents remote attacker “workstation-as-a-proxy” attacks
- Prevents unauthorized session continuation after user stops interacting