Introduction
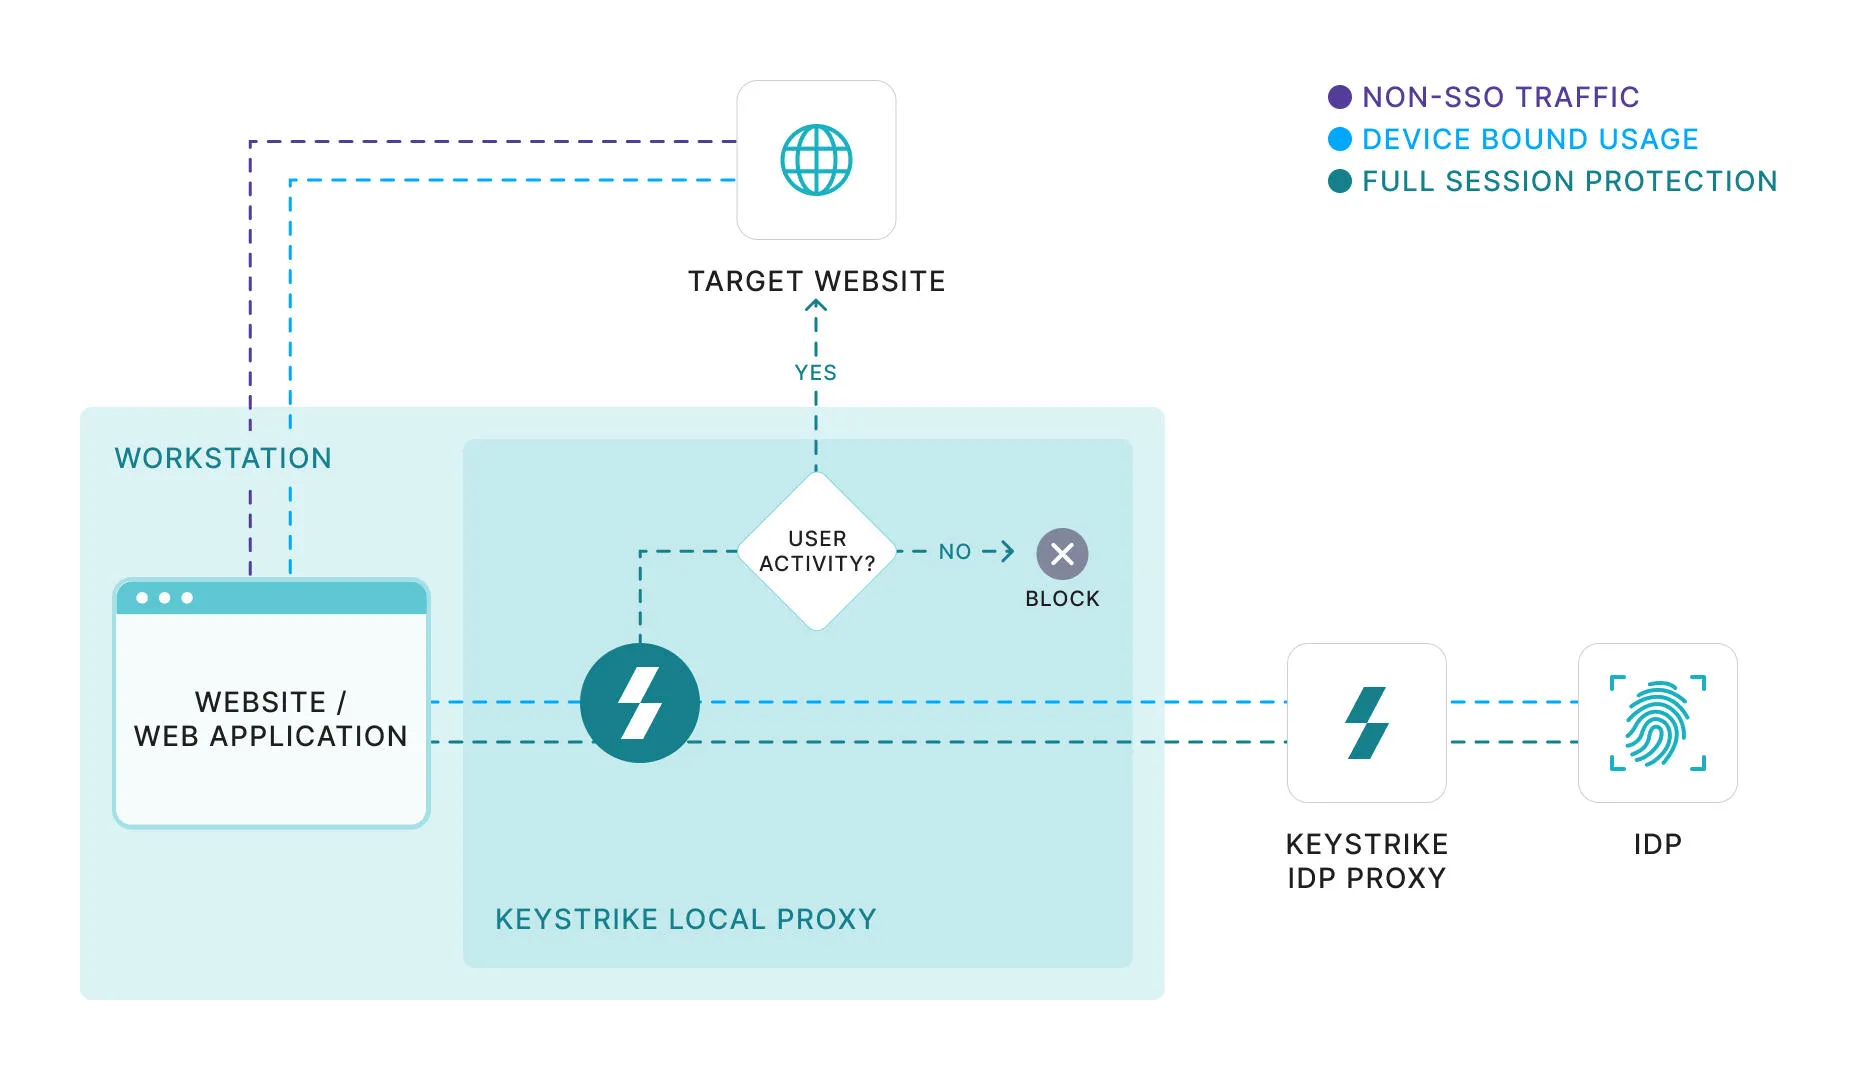
Keystrike Cloud Protector includes two main components: a Local Proxy installed on employee workstations, and a central IDP Proxy that manages the organization's identity provider (IDP) single sign-on (SSO) requests.
Web traffic from an employee's workstation can be categorized into one of three types, each handled differently:
- A. Non-SSO traffic
- B. SSO - Device Bound Usage
- C. SSO - Full Session Protection
A. Non-SSO traffic
Websites that do not require SSO authentication are unaffected as they are not routed through the Local Proxy.
B. SSO - Device Bound Usage
For SSO-enabled applications that are not within the set of webapps having full session protection, authentication requests are routed through the Local Proxy and IDP Proxy before reaching the IDP. This ensures that all SSO web applications benefit from added security, as the authentication is tied to both the user and the device—making stolen authentication cookies or tokens unusable outside that context. Once authentication is complete, subsequent traffic to the web application bypasses the Local Proxy.
Protection level: Defends against credential theft and prevents authentication or session reuse from unauthorized devices.
C. SSO - Full Session Protection
For sensitive or high-value SaaS applications, KeyStrike provides continuous session enforcement in addition to device binding the authentication.
- All subsequent traffic is routed through the Local Proxy.
- Each request is checked for recent user input (keyboard, mouse) in addition to device integrity.
- If the user becomes inactive or the device fails validation, access is immediately blocked.
This ensures that only an active, authorized user on a trusted device can maintain a session.
Protection level: Prevents idle-device abuse, session hijacking, and unauthorized session continuation.